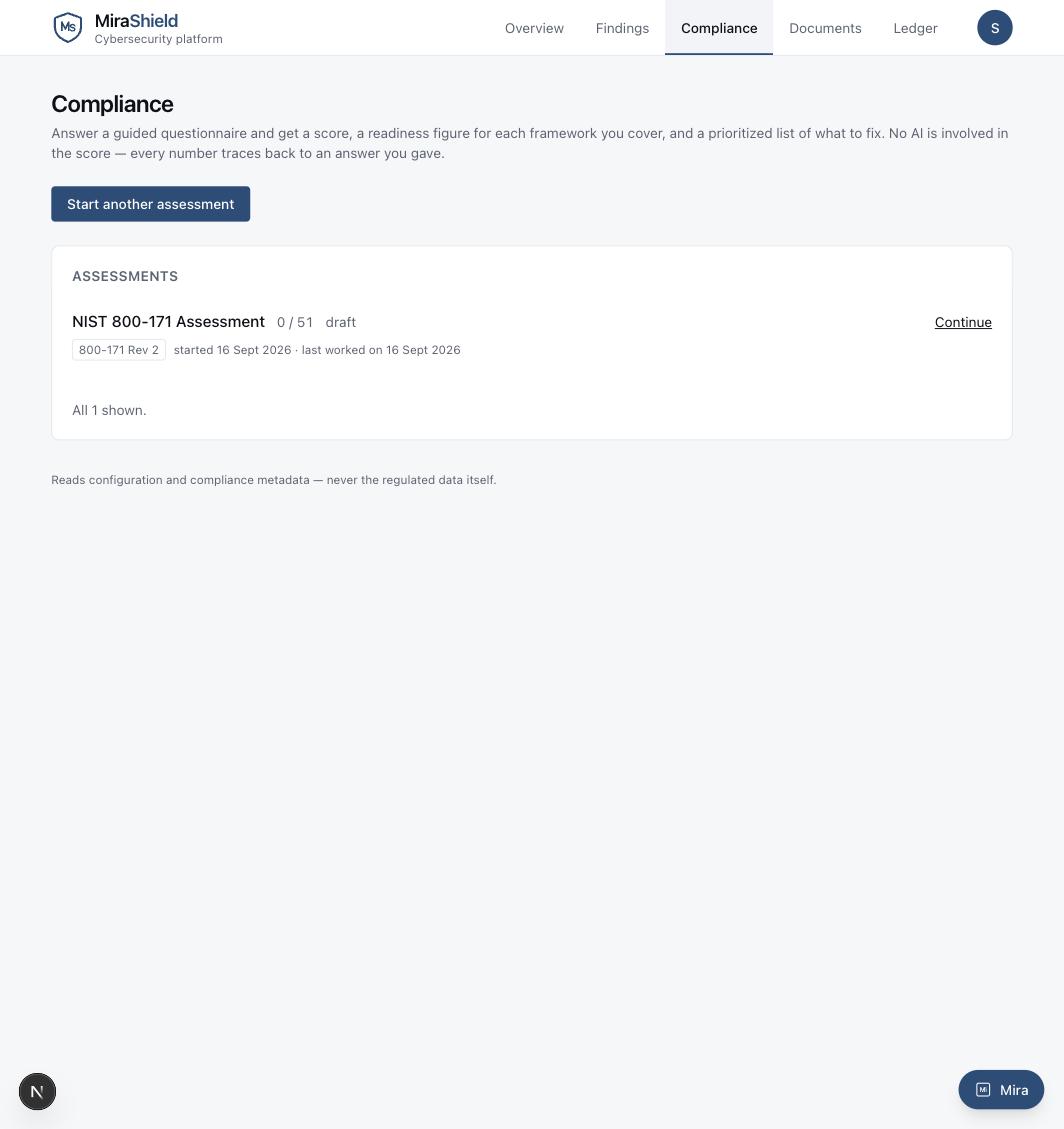
SPRS, Rev 3 readiness, and the gap report — where every number comes from.
No AI is involved in scoring. Every status is computed from your own answers by rules held in a table, so any number can be explained by pointing at the answers that produced it — the same answers always produce the same score, on this deployment or anyone else's.
Every assessment you've started, with how far along it is — pick one up from here whenever you return.
How to use it
The SPRS score follows the DoD Assessment Methodology's own weight table — 1, 3, or 5 points per requirement, not an estimate.
Each framework you selected gets its own readiness figure, because "compliant" means something different under CMMC L2 than under HIPAA.
The gap report is prioritized, not alphabetical: ordered by risk first, then by how much effort each fix takes — so the top of the list is genuinely where to start.
Every gap names the specific answer that produced it. There is no gap on this list you cannot trace back to something you told the questionnaire.
ISO 27001 also asks for a risk register — a list of what could go wrong, who owns it, what you decided. That has no fixed set of answers to pick from, so it lives on its own screen rather than inside the questionnaire; see Settings for the register once ISO 27001 is one of your frameworks.